Tag: access control

  • Zero Trust for Australian Organisations: A Practical Migration Guide

    Zero Trust for Australian Organisations: A Practical Migration Guide

    Reviewed: 13 September 2026 · Next review: 13 December 2026
    Author: Ozlin Info Editorial Team · Human review: Lin (accountable human); Codex assisted

    Zero trust is not a product, a VPN replacement or a requirement to interrupt people with a new login prompt every few minutes. It is an architecture and operating approach that removes implicit trust based only on network location, device ownership or organisational affiliation.

    NIST SP 800-207 defines zero trust around users, assets and resources. Authentication and authorisation occur before a session to a protected resource is established, and policy decisions use available evidence rather than treating “inside the network” as sufficient proof (NIST SP 800-207).

    ASD now places zero trust within its modern defensible architecture guidance alongside layered architecture and secure-by-design practices. Its foundations describe three principles: never trust, always verify; assume breach; and verify explicitly (ASD — Foundations for modern defensible architecture).

    Start with the resource and business decision

    A weak zero trust programme begins by buying tools. A stronger one begins by identifying a business resource and writing the access decision that must be enforced.

    For example:

    Finance records may be accessed by a current finance worker using an approved account and compliant managed device for an authorised task. High-risk sessions require stronger evidence or are denied. Privileged changes use a separate role and are logged.

    That statement exposes the required capabilities: reliable identity, device information, resource ownership, policy, enforcement, logging, exception handling and recovery. It also gives the organisation something testable.

    Do not try to transform every system at once. Select a workflow where the resource, users, risks and dependencies are understood. Common pilots include privileged administration, contractor access, a cloud application containing sensitive data or an internal application currently reachable by a broad network group.
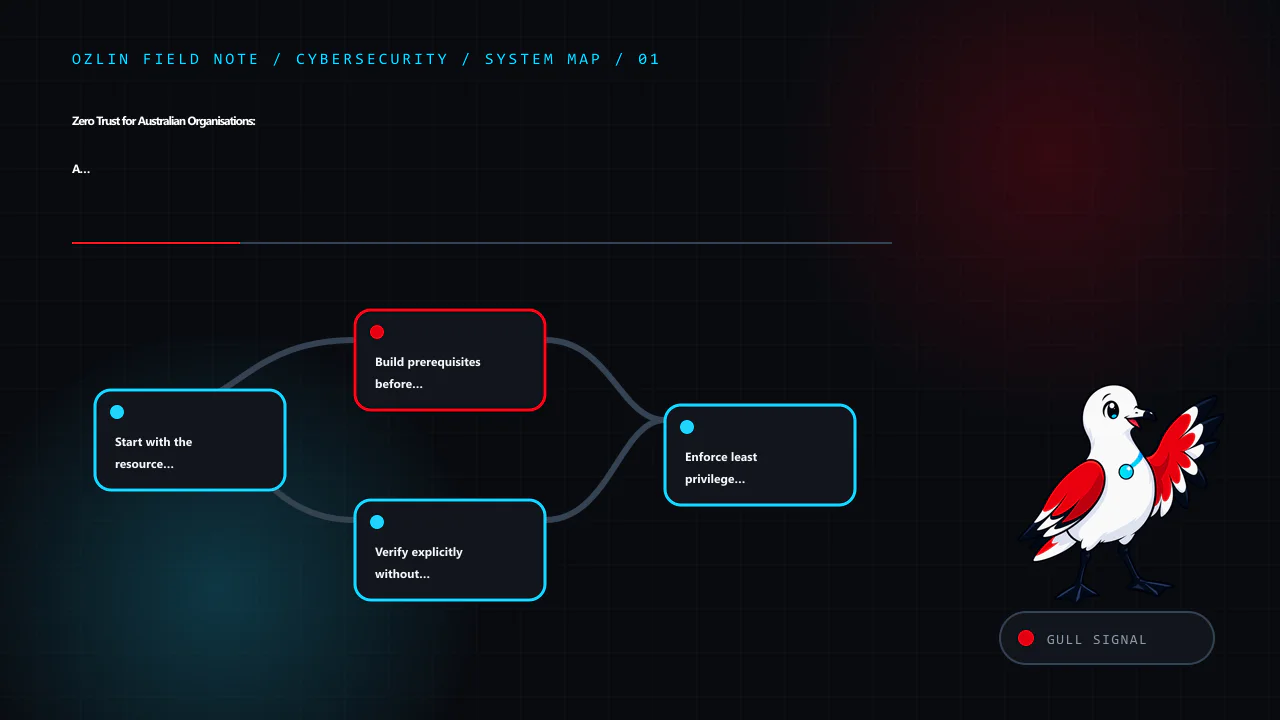
    Article map for Zero Trust for Australian Organisations: A Practical Migration Guide, covering Start with the resource and business decision, Build prerequisites before dynamic policy, Verify explicitly without creating…
    Article map: Start with the resource and business decision; Build prerequisites before dynamic policy; Verify explicitly without creating permanent friction; Enforce least privilege at several layers.

    Build prerequisites before dynamic policy

    Zero trust decisions are only as reliable as their inputs. Establish:

    • an inventory of important resources, data and services;
    • named business and technical owners;
    • unique human, workload and device identities;
    • controlled account lifecycle and prompt removal of stale access;
    • device registration and meaningful posture signals where appropriate;
    • data classification that can influence access decisions;
    • central policy and change control; and
    • logs that allow a decision to be reconstructed.

    If a directory contains shared accounts, devices cannot be identified and no one owns the application, a highly dynamic policy may add complexity without adding assurance.

    Verify explicitly without creating permanent friction

    Explicit verification means using evidence appropriate to the requested action. Evidence can include:

    • identity and authentication strength;
    • device identity, management and security posture;
    • requested resource and action;
    • user, service or workload role;
    • location, network and time as contextual signals—not sole proof;
    • recent risk events or impossible behaviour;
    • data sensitivity; and
    • session and transaction risk.

    Phishing-resistant MFA is valuable for high-impact access, but zero trust is larger than MFA. Likewise, conditional access is not useful if emergency accounts, service identities, API keys and legacy protocols bypass it.

    Good design reduces unnecessary prompts by reusing strong, current evidence and raising requirements when risk or consequence changes. It should remain possible to explain why access was allowed, denied or escalated.
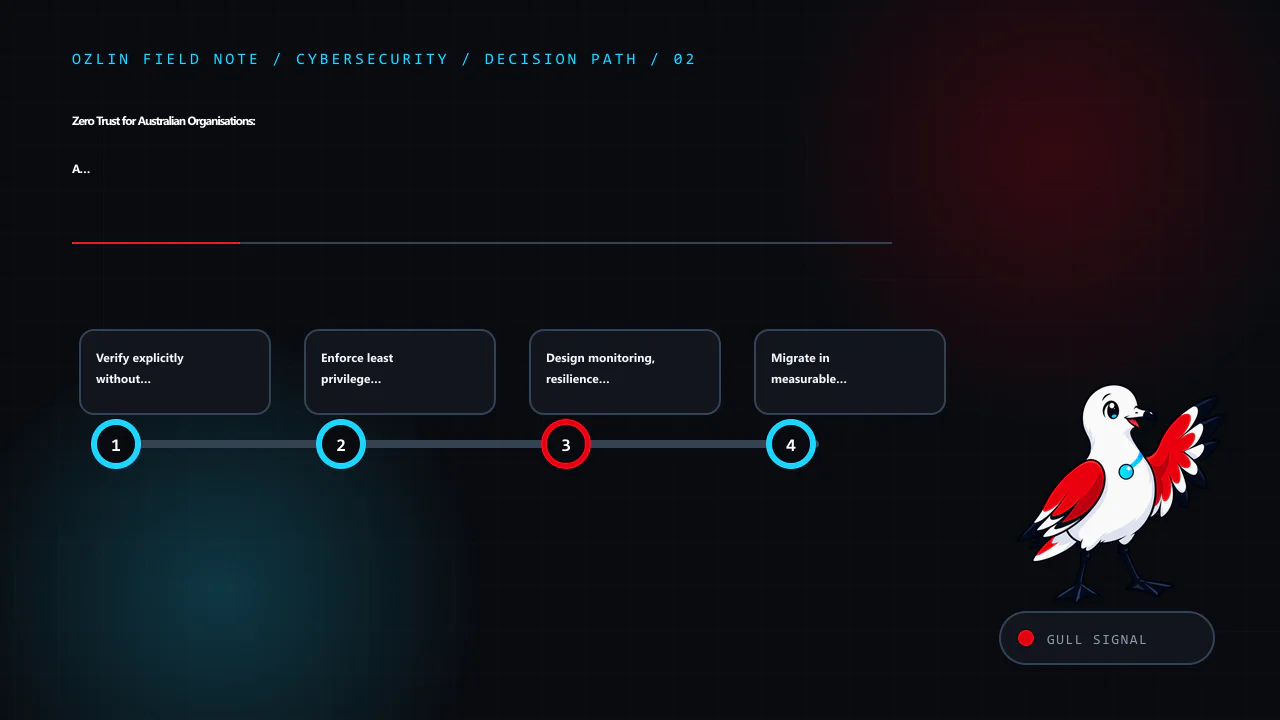
    Decision path for Zero Trust for Australian Organisations: A Practical Migration Guide, covering Verify explicitly without creating permanent friction, Enforce least privilege at several layers, Design monitoring, resil…
    Decision path: Verify explicitly without creating permanent friction; Enforce least privilege at several layers; Design monitoring, resilience and exceptions together; Migrate in measurable increments.

    Enforce least privilege at several layers

    Least privilege should cover people, administrators, applications, machines and automated agents. Review both standing access and what can be requested temporarily.

    Useful controls include:

    • role or attribute-based access tied to a defined job;
    • just-in-time elevation for high-impact administration;
    • separate routine and privileged identities;
    • workload identities instead of embedded shared secrets;
    • resource-specific application and API permissions;
    • approval and logging for exceptional access; and
    • automatic expiry where the business need is temporary.

    Micro-segmentation can reduce lateral movement, but it is one possible capability—not the definition of zero trust and not mandatory in the same form for every environment. NIST SP 800-207A shows how cloud-native access can focus on application and service identity in addition to network controls (NIST SP 800-207A).

    Design monitoring, resilience and exceptions together

    Policy engines, identity providers, device services and enforcement points become critical dependencies. Plan what happens when one is unavailable or supplies stale information. A zero trust programme that locks out every responder during an incident is not resilient.

    Document:

    • high-availability and recovery requirements;
    • protected emergency access with independent monitoring;
    • safe behaviour when a dependency is unavailable;
    • alert ownership and expected response;
    • policy versioning and rollback;
    • how false denials and false allowances are investigated; and
    • how compromised identities or devices are revoked quickly.

    “Assume breach” means designing so one compromised account or device does not automatically reach every resource. It does not mean assuming every employee is malicious or blocking work without evidence.
    Control and evidence map for Zero Trust for Australian Organisations: A Practical Migration Guide, covering Design monitoring, resilience and exceptions together, Migrate in measurable increments, Treat legacy systems a…
    Control and evidence map: Design monitoring, resilience and exceptions together; Migrate in measurable increments; Treat legacy systems as explicit risk; General-information disclaimer.

    Migrate in measurable increments

    A practical sequence is:

    1. Discover: map the selected workflow, resources, identities, data and current trust assumptions.
    2. Define: write the intended access rules, evidence, exceptions and owners.
    3. Observe: collect data without blocking to identify unexpected dependencies and policy errors.
    4. Pilot: enforce for a limited population with support and rollback available.
    5. Validate: test expected access, denial, elevation, revocation, outage and recovery cases.
    6. Expand: add resources only after the operating model works.

    Useful measures include:

    Measure Evidence
    Resource coverage Important resources with named owners and explicit policy
    Identity hygiene Shared, dormant and excessive accounts removed
    Privilege exposure Standing high-impact access converted or justified
    Revocation Time to remove access across connected systems
    Decision quality Sampled allow/deny decisions supported by expected evidence
    User impact Failed legitimate access, support effort and workaround attempts
    Resilience Successful identity/policy outage and emergency-access exercise

    Do not claim that a drop in breaches proves the zero trust programme caused it. Security incidents are sparse, affected by exposure and detection, and not a clean single-control metric.

    Treat legacy systems as explicit risk

    Some systems cannot consume modern identity, device or workload signals. Record the limitation, business need, compensating controls, monitoring, owner and retirement or upgrade date. A network gateway may provide a temporary policy boundary, but it does not magically give the legacy application resource-level authorisation.

    Use current ASD modern defensible architecture guidance rather than the obsolete “DSD” wording in the original article. Also avoid saying that zero trust itself proves Privacy Act, APRA, ISO or other compliance. It may support control objectives; applicability and compliance require separate assessment and evidence.

    For help mapping an identity, website, cloud or administration workflow into a scoped access-control roadmap, see Ozlin Info's cybersecurity services or contact Ozlin Info.

    Related reading: Cybersecurity fundamentals for business risk.

    Practical checklist for Zero Trust for Australian Organisations: A Practical Migration Guide, covering Treat legacy systems as explicit risk, General-information disclaimer, AI-assistance disclosure and related review p…
    Practical checklist: Treat legacy systems as explicit risk; General-information disclaimer; AI-assistance disclosure; Primary sources checked.

    General-information disclaimer

    This article provides general technical information only. It is not architecture, legal, privacy, regulatory or compliance advice and does not define a complete zero trust implementation. Appropriate policy and controls depend on the organisation, data, systems, users, risks and obligations.

    Limitations: Zero-trust migration depends on legacy constraints, identity and device signals, architecture, user impact, funding and measured tests. These steps do not guarantee security or compliance.

    AI-assistance disclosure

    AI tools assisted with source discovery, outlining and copyediting. The recorded editorial review and review schedule appear at the start of this article. Verify current sources and project-specific assumptions before relying on this guidance. No security or compliance outcome is guaranteed.

    Primary sources checked

    Source access date: 29 August 2026.
  • Cybersecurity Fundamentals for Small Business Owners

    Cybersecurity Fundamentals for Small Business Owners

    Reviewed: 13 September 2026 · Next review: 13 December 2026
    Author: Ozlin Info Editorial Team · Human review: Lin (accountable human); Codex assisted

    Cybersecurity becomes easier to manage when it is translated from technical products into business questions:

    • What services and information matter?
    • What could go wrong, and what would the impact be?
    • Who owns the decision?
    • Which safeguards are proportionate?
    • How will we know they are operating?
    • How will the business respond and recover when prevention is not enough?

    These are fundamentals because they remain useful when products, threats and business models change. They also prevent a common mistake: buying a tool before defining the problem it is supposed to reduce.

    Begin with business outcomes and risk

    A risk discussion needs context. A public brochure website, an accounting platform, a developer's source-code repository and a health-services booking system do not have the same data, dependencies or consequences.

    List the activities the business must continue and the technology, people, data and suppliers that support them. For each important scenario, describe the plausible business impact: interrupted delivery, fraudulent payment, lost records, exposed personal information, unsafe decisions, contractual breach or reputational harm. Estimate likelihood only as carefully as the available evidence allows; false precision does not improve the decision.

    Record a responsible owner and a chosen treatment. The business might reduce the risk, avoid the activity, transfer some financial consequences through contract or insurance, or consciously accept residual risk. Acceptance should be an informed business decision with a review date—not what happens silently when nobody acts.

    NIST describes its Cybersecurity Framework 2.0 as a taxonomy of high-level outcomes for organisations of any size to understand, assess, prioritise and communicate cybersecurity work. The framework is deliberately non-prescriptive: it describes desired outcomes rather than requiring one product or implementation (NIST CSF 2.0).

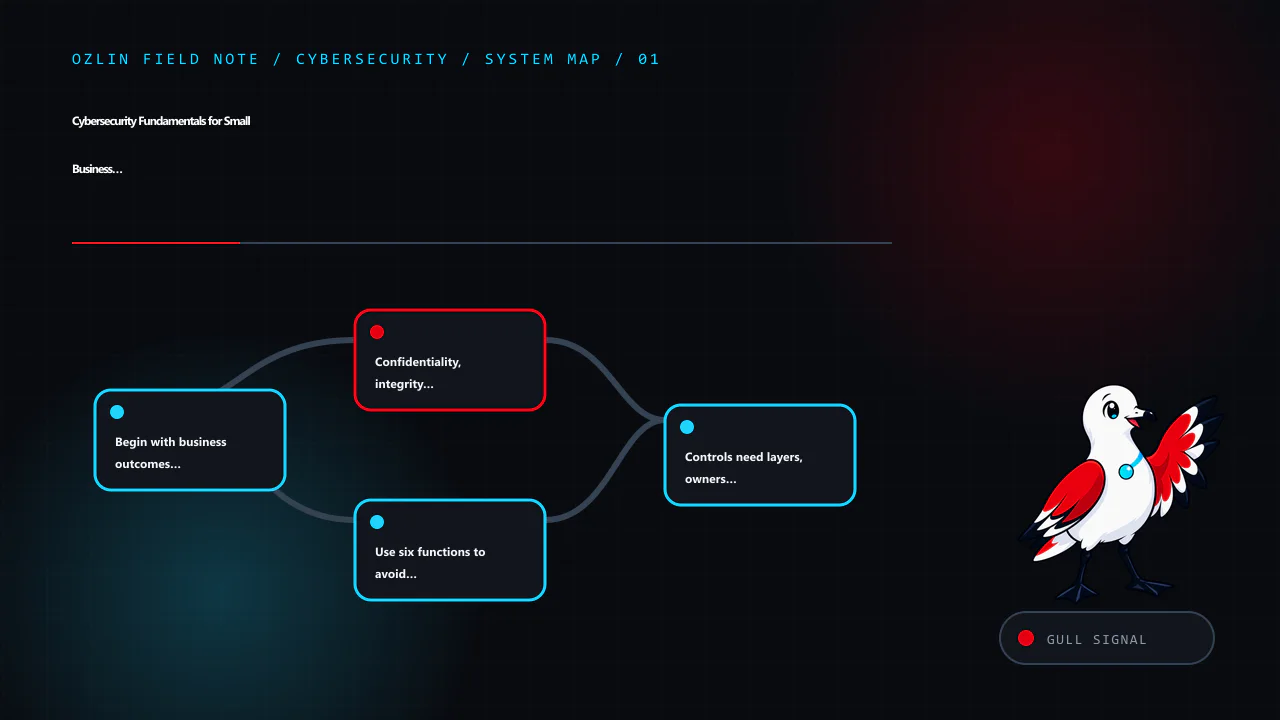
    Article map for Cybersecurity Fundamentals for Small Business Owners, covering Begin with business outcomes and risk, Confidentiality, integrity and availability, Use six functions to avoid prevention-only security and…
    Article map: Begin with business outcomes and risk; Confidentiality, integrity and availability; Use six functions to avoid prevention-only security; Controls need layers, owners and evidence.

    Confidentiality, integrity and availability

    Three enduring security objectives are confidentiality, integrity and availability, often shortened to CIA (NIST glossary). In practical terms:

    • Confidentiality: information is not disclosed to people or systems that should not receive it. Examples include protecting credentials and limiting access to client records.
    • Integrity: information and systems are accurate and changed only in authorised ways. Examples include detecting altered bank details, unauthorised website changes or tampered backups.
    • Availability: authorised users can access the service or information when the business needs it. Examples include recovering invoices after device failure or continuing customer communication during an email outage.

    The priorities vary by service. Encryption can protect confidentiality in storage or transit, but it does not ensure that a compromised authorised account uses the data correctly. A backup can support availability, but an untested or attacker-accessible backup may not recover the business. A control should be connected to a specific objective and failure scenario.

    Other concepts fit around the same model. Identification claims who a user or system is. Authentication checks that claim. Authorisation decides what the authenticated identity may do. Accountability depends on records that are reliable enough to connect important actions with identities and time. None of these should be described as absolute “non-repudiation” unless the specific technical and legal context supports that conclusion.

    Use six functions to avoid prevention-only security

    NIST CSF 2.0 groups outcomes into six concurrent functions: Govern, Identify, Protect, Detect, Respond and Recover. Govern was made explicit in version 2.0 because cybersecurity risk belongs in organisational decision-making, alongside operational, financial and reputational risk (NIST CSF 2.0 overview).

    For a small business, the functions can be translated as follows:

    1. Govern: set risk ownership, priorities, policy, supplier expectations and relevant legal or contractual obligations.
    2. Identify: know critical assets, data flows, dependencies, vulnerabilities and plausible threats.
    3. Protect: apply safeguards such as MFA, least privilege, secure configuration, patching, backups and staff procedures.
    4. Detect: collect and review useful signals, including privileged sign-ins, backup failures and unexpected account or data changes.
    5. Respond: assess, contain, communicate, preserve evidence and coordinate the people needed during an incident.
    6. Recover: restore services and information, communicate appropriately and improve the plan from lessons learned.

    The functions happen together. Recovery cannot wait until after an incident to be designed, and detection cannot be improvised from logs that were never enabled.

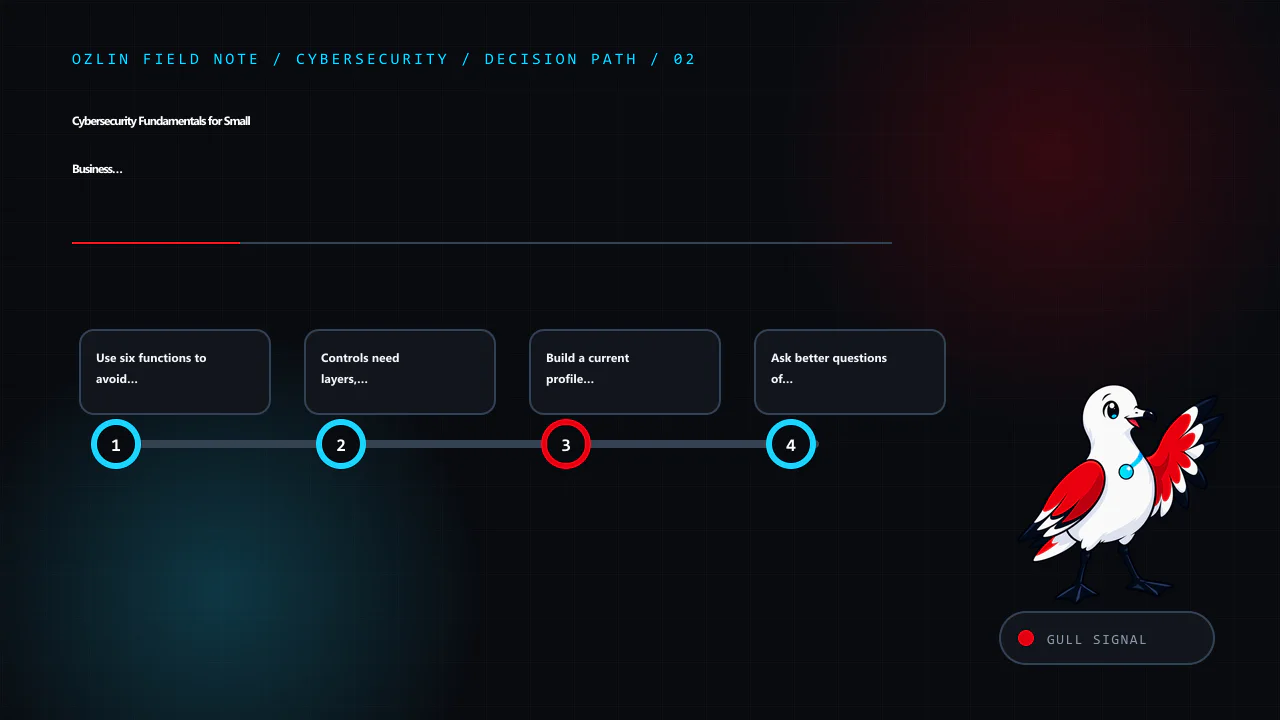
    Decision path for Cybersecurity Fundamentals for Small Business Owners, covering Use six functions to avoid prevention-only security, Controls need layers, owners and evidence, Build a current profile and a target profi…
    Decision path: Use six functions to avoid prevention-only security; Controls need layers, owners and evidence; Build a current profile and a target profile; Ask better questions of suppliers and security tools.

    Controls need layers, owners and evidence

    Controls can be administrative, technical or physical. A payment-fraud risk might be reduced by a written approval process, independent callback, role-based access, email protections and staff reporting. If one layer fails, another can still limit harm.

    Avoid treating familiar tools as complete solutions:

    • A firewall filters defined traffic; it does not make an allowed application secure.
    • Endpoint security can detect some malicious activity; it does not prove an endpoint is uncompromised.
    • A VPN protects a connection in particular circumstances; it does not make an untrusted device or fraudulent website safe.
    • Encryption protects data under defined conditions; it does not correct excessive access or a stolen authorised session.
    • Training supports decisions; it should not be the only control protecting a high-value payment.

    Every important control needs an owner, an expected operating state and evidence. Evidence might be a current access review, a successful restore test, patch-status records, a verified alert, an incident-exercise result or a supplier report. ASD's Essential Eight assessment guidance emphasises credible evidence when assessing both implementation and control effectiveness (ASD's ACSC Essential Eight assessment process guide).

    Build a current profile and a target profile

    A practical first assessment can fit in a short table:

    Business outcome Current state Target state Evidence Owner Due date
    Important accounts resist password theft MFA varies by service MFA on all high-impact accounts; recovery methods reviewed Provider export and access review Operations owner Set locally
    Critical records can be restored Backups report success A clean restore is demonstrated within the required time Dated restore-test record System owner Set locally
    Payment changes are independently verified Informal checking Known-number callback and second approval Sampled approval record Finance owner Set locally
    Incidents can be escalated Contacts are scattered Offline contact list and exercised response plan Exercise notes and actions Business owner Set locally

    NIST calls these Current and Target Profiles. Comparing them helps expose gaps and build an action plan aligned with business needs, risk tolerance and resources (NIST CSF frequently asked questions). Do not copy somebody else's target blindly; sector obligations, client contracts, technical complexity and threat exposure can justify a different outcome.

    Control and evidence map for Cybersecurity Fundamentals for Small Business Owners, covering Build a current profile and a target profile, Ask better questions of suppliers and security tools, Establish a small operating…
    Control and evidence map: Build a current profile and a target profile; Ask better questions of suppliers and security tools; Establish a small operating rhythm; General-information disclaimer.

    Ask better questions of suppliers and security tools

    Before buying a product or managed service, ask:

    • Which documented risk and target outcome does this address?
    • What data and administrator access will the supplier receive?
    • How are privileged actions authenticated and logged?
    • What happens when the supplier or integration is unavailable?
    • How are vulnerabilities, incidents and material changes communicated?
    • Can the business export its data and logs in a usable form?
    • What evidence will show that the control works after deployment?
    • Who remains responsible for configuration, monitoring and recovery?

    A contract can allocate tasks, but outsourcing does not remove the need to understand critical dependencies. NIST's small-business material similarly recommends considering business objectives, high-value assets, obligations and dependencies before deciding whether to build capability internally or outsource it (NIST small-business team guidance).

    Establish a small operating rhythm

    Security improves through repeated, owned work:

    • Monthly: review critical alerts, failed backups, privileged accounts, new integrations and overdue high-priority actions.
    • Quarterly or risk-based: test a restore, review access, sample payment verification and rehearse one incident scenario.
    • On material change: review risks when adopting a new SaaS platform, collecting new data, exposing a service to the internet or changing a critical supplier.
    • After an incident or exercise: record what happened, which assumptions failed and which change has an owner and date.

    The related Australian SME cybersecurity baseline turns these principles into an implementation sequence. The phishing response playbook covers one common scenario in more depth.

    For help defining a proportionate target state and evidence plan, see Ozlin Info's cybersecurity uplift service or contact Ozlin Info.


    Practical checklist for Cybersecurity Fundamentals for Small Business Owners, covering Establish a small operating rhythm, General-information disclaimer, AI-assistance disclosure and related review points.
    Practical checklist: Establish a small operating rhythm; General-information disclaimer; AI-assistance disclosure; Primary sources checked.

    General-information disclaimer

    This article provides general information only. It is not legal, privacy, insurance, compliance, financial or incident-response advice, and it does not establish that any control set is sufficient for a particular organisation. Appropriate safeguards depend on your data, systems, contracts, sector, threat exposure and risk decisions.

    Limitations: Framework concepts do not establish a complete control set or a measured reduction in risk. Effectiveness depends on implementation, evidence, threat environment, resources, supplier dependencies and business priorities.

    AI-assistance disclosure

    AI tools assisted with outlining and copyediting this article. The recorded editorial review and review schedule appear at the start of this article. Verify current sources and project-specific assumptions before relying on this guidance. The article avoids product endorsements and does not promise prevention or compliance.

    Primary sources checked

    Source access date: 28 August 2026.