Tag: incident response

  • Incident Response and Disaster Recovery: A Practical Australian Playbook

    Incident Response and Disaster Recovery: A Practical Australian Playbook

    Reviewed: 13 September 2026 · Next review: 13 December 2026
    Author: Ozlin Info Editorial Team · Human review: Lin (accountable human); Codex assisted

    Incident response and disaster recovery are related, but they are not interchangeable. An organisation can contain an attacker and still be unable to operate. It can also restore a server quickly while restoring the same compromise, losing evidence or making an unapproved public statement.

    A useful plan connects four disciplines:

    • cyber incident response — detecting, analysing, containing, remediating and learning from a security incident;
    • business continuity — maintaining the organisation's critical activities during disruption;
    • disaster recovery — restoring technology and data to an acceptable state; and
    • crisis communication and decision-making — coordinating leaders, workers, suppliers, customers, regulators and other stakeholders.

    The previous version of this article asserted that breaches are inevitable, quoted an unverified average Australian breach cost and prescribed quarterly testing for every organisation. Those claims are removed. Risk, impact and exercise frequency depend on the organisation and its obligations; readiness should be demonstrated by evidence, not fear-based statistics.

    Prepare before the alert arrives

    ASD's current practitioner guidance says a cyber incident response plan should align with emergency, crisis, business continuity and disaster-recovery arrangements, be tailored to the environment, and be regularly tested and reviewed (ASD — Cyber security incident response planning).

    Begin with decision rights and reliable contact paths. Record:

    • the incident lead and deputy;
    • technical, business, legal/privacy and communications decision-makers;
    • critical service owners and recovery priorities;
    • cyber insurer or broker contacts and relevant policy conditions;
    • hosting, cloud, identity, banking and managed-service escalation paths;
    • law-enforcement and government reporting routes where relevant;
    • who can isolate systems, disable accounts, restore data and approve public statements; and
    • an offline, protected copy of the plan and key contacts.

    Create short playbooks for likely scenarios such as phishing/business email compromise, compromised administrator access, ransomware, lost devices, website compromise, cloud-key exposure and data breach. A playbook should support judgement; it should not force responders to follow a damaging action merely because it appears as step three.
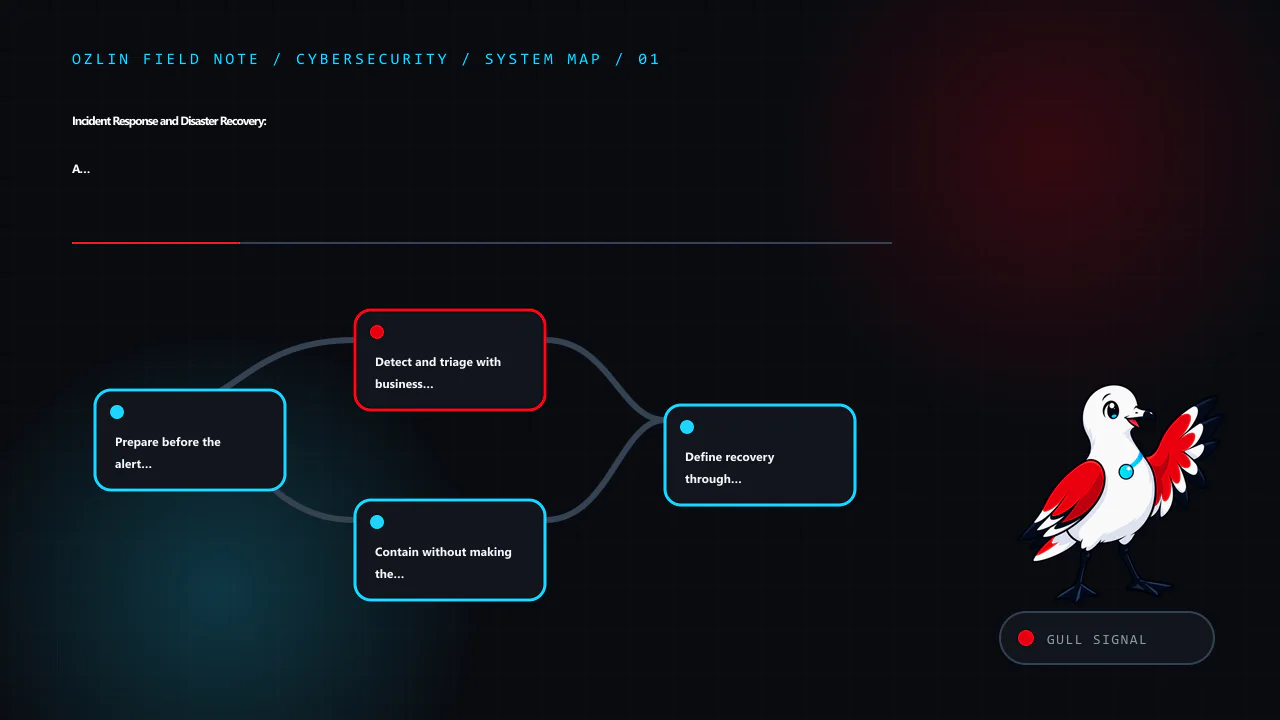
    Article map for Incident Response and Disaster Recovery: A Practical Australian Playb…, covering Prepare before the alert arrives, Detect and triage with business context, Contain without making the situation worse and…
    Article map: Prepare before the alert arrives; Detect and triage with business context; Contain without making the situation worse; Define recovery through business impact.

    Detect and triage with business context

    Define how workers and suppliers report a concern at any time. Record the first observation, source, time, affected accounts or services and actions already taken. Establish an incident log early and preserve the original alert, relevant timestamps and decision rationale.

    Triage should ask:

    1. What is known and what is only suspected?
    2. Which identities, data, systems and business processes may be affected?
    3. Is the activity ongoing?
    4. Could a containment action disrupt a critical service or destroy evidence?
    5. Who has authority to make the next decision?
    6. Is specialist incident-response, legal, privacy, insurer or law-enforcement help required now?

    NIST SP 800-61 Rev.3, finalised in April 2025, integrates incident response across the Govern, Identify, Protect, Detect, Respond and Recover functions of the Cybersecurity Framework 2.0 rather than treating response as an isolated technical phase (NIST SP 800-61 Rev.3).
    Decision path for Incident Response and Disaster Recovery: A Practical Australian Playb…, covering Detect and triage with business context, Contain without making the situation worse, Define recovery through business im…
    Decision path: Detect and triage with business context; Contain without making the situation worse; Define recovery through business impact; Handle notification as a scoped decision.

    Contain without making the situation worse

    “Isolate everything immediately” is not a universal rule. Isolation may be appropriate, but responders should consider operational impact, evidence preservation, attacker visibility and the time required for a safer alternative. ASD's guidance explicitly asks organisations to consider the additional effects, duration and effectiveness of containment options.

    Possible authorised actions include disabling a compromised session, account, API key or forwarding rule; restricting network access; blocking a malicious indicator; preserving a system image or relevant logs; and moving a critical service to a known-clean path. The exact action depends on the incident and must stay within legal authority and the agreed response role.

    Do not delete logs, wipe a system or “hack back”. Protect collected evidence from unnecessary access and record who collected it, when, from where and how its integrity was maintained. Engage a qualified forensic specialist where evidence may support litigation, insurance, employment or regulatory decisions.

    Define recovery through business impact

    Recovery objectives should be based on the business processes a system supports. NIST's contingency-planning guide distinguishes:

    • maximum tolerable downtime (MTD): the total outage or disruption the process can tolerate;
    • recovery time objective (RTO): the maximum time a system resource can remain unavailable before unacceptable impact; and
    • recovery point objective (RPO): the point in time to which data must be recoverable, which expresses tolerable data loss (NIST SP 800-34 Rev.1).

    Do not copy a supplier's advertised recovery figure into the plan without validating dependencies. A website may depend on DNS, identity, secrets, database, storage, mail, payment, third-party APIs and staff access. Recovery should specify the order, prerequisites, owners and acceptance tests.

    A safe recovery sequence normally includes:

    1. approve a remediation and recovery plan;
    2. establish a known-clean identity and administration path;
    3. remediate the entry point and affected trust relationships;
    4. restore systems and data from an appropriate source;
    5. rotate exposed credentials and keys according to impact;
    6. validate integrity, security configuration and business function;
    7. monitor for recurrence or missed persistence; and
    8. obtain accountable approval before returning to normal operation.

    A backup is not recovery evidence. Run restoration exercises, record duration and missing dependencies, and protect recovery administration from the identities used for everyday work.
    Control and evidence map for Incident Response and Disaster Recovery: A Practical Australian Playb…, covering Define recovery through business impact, Handle notification as a scoped decision, Exercise the decisions, no…
    Control and evidence map: Define recovery through business impact; Handle notification as a scoped decision; Exercise the decisions, not just the document; General-information disclaimer.

    Handle notification as a scoped decision

    Not every security event is a notifiable data breach, and not every Australian organisation has the same obligations. The OAIC's current quick-reference guide applies to entities covered by the Notifiable Data Breaches scheme and uses a contain–assess–notify if required–review sequence (OAIC — Responding to data breaches).

    Assess coverage, the information involved, likely serious harm, remedial action and statutory timeframes with appropriate advice. Preserve the basis for the decision. Sector-specific obligations can also apply. For example, APRA's CPS 230 and CPS 234 apply to APRA-regulated entities, not to every Australian business (APRA — CPS 230). Contractual, insurer, customer and platform notification requirements may be separate again.

    Report active cybercrime or incidents through the appropriate official channel when relevant. Do not delay urgent containment solely to perfect a report, but do not make unsupported public attribution or promise an outcome before facts are established.

    Exercise the decisions, not just the document

    Choose exercise frequency from risk, change, obligations and prior findings rather than a universal quarterly rule. Useful exercise types include:

    • a contact-tree and escalation test;
    • a tabletop decision exercise;
    • a technical restore test;
    • a failover or alternate-workflow exercise; and
    • a combined incident, recovery and communications simulation.

    Define observable acceptance criteria: contacts reached within the expected window, correct authority identified, evidence preserved, backup restored, critical transaction completed, notification question escalated and unresolved actions assigned.

    After an incident or exercise, run a blameless review that still assigns ownership. Update the plan, architecture, controls, supplier agreements and funded work backlog. An incident is not “closed” merely because production is available again.

    For a scoped review of response roles, backups, restoration evidence and website/cloud dependencies, see Ozlin Info's cybersecurity services or contact Ozlin Info.

    Related reading: Phishing response playbook for Australian businesses.

    Practical checklist for Incident Response and Disaster Recovery: A Practical Australian Playb…, covering Exercise the decisions, not just the document, General-information disclaimer, AI-assistance disclosure and relate…
    Practical checklist: Exercise the decisions, not just the document; General-information disclaimer; AI-assistance disclosure; Primary sources checked.

    General-information disclaimer

    This article provides general information only. It is not incident-response, forensic, legal, privacy, regulatory, insurance or business-continuity advice. Actions and notification obligations depend on the facts, authority, systems, information, contracts, sector and jurisdiction. Seek urgent qualified help when an incident may be active.

    Limitations: A generic response sequence cannot replace a current plan, forensic advice or an incident commander. Recovery and notification outcomes depend on facts, contracts, jurisdiction and tested capabilities.

    AI-assistance disclosure

    AI tools assisted with source discovery, outlining and copyediting. The recorded editorial review and review schedule appear at the start of this article. Verify current sources and project-specific assumptions before relying on this guidance. No recovery time or incident outcome is promised.

    Primary sources checked

    Source access date: 29 August 2026.
  • Cyber Insurance for Australian Small Businesses: A Reading Checklist

    Cyber Insurance for Australian Small Businesses: A Reading Checklist

    Cyber insurance transfers defined financial risks under a contract. It does not make an insecure system safe, guarantee that every incident is covered or replace legal, privacy, continuity and incident-response work. Two products carrying the same label can differ materially in definitions, triggers, exclusions, sublimits, excesses and response providers.

    For an Australian small business, the practical task is to map its own loss scenarios, read the complete policy pack and rehearse how a claim would begin. Premium anecdotes and headline coverage figures cannot do that work.

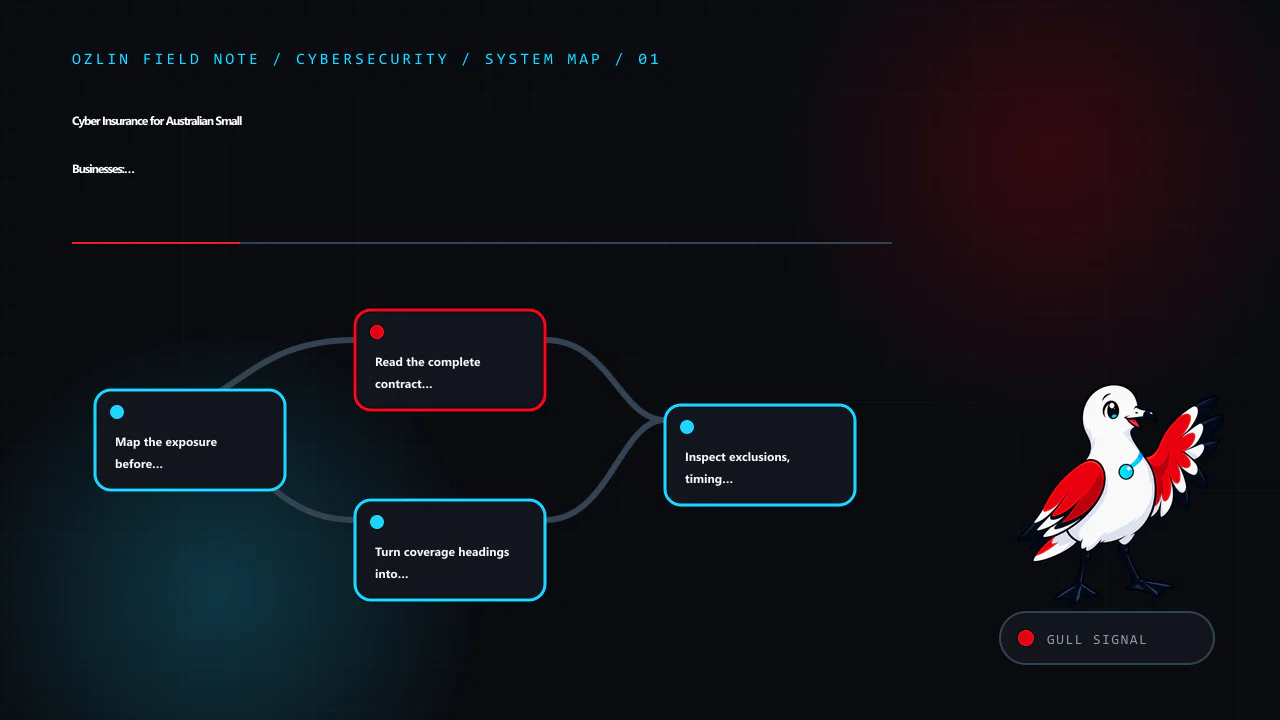
    Article map for Cyber Insurance for Australian Small Businesses: A Reading Checklist, covering Map the exposure before asking for a quote, Read the complete contract stack, Turn coverage headings into questions and rela…
    Article map: Map the exposure before asking for a quote; Read the complete contract stack; Turn coverage headings into questions; Inspect exclusions, timing and aggregation.

    Map the exposure before asking for a quote

    Describe the systems and dependencies that could stop revenue, expose data or create liability:

    • customer, employee, payment and credential data held by the business or a provider;
    • websites, cloud tenants, email, endpoints, backups and remote access;
    • outsourced hosting, managed services, software and payment platforms;
    • maximum tolerable downtime and critical manual workarounds;
    • contractual security, notification and indemnity commitments; and
    • plausible events such as business email compromise, ransomware, accidental disclosure, provider outage or stolen credentials.

    Estimate losses by scenario rather than choosing a round limit. Separate restoration and specialist-response cost, lost gross profit, extra expense, customer or regulator communication, third-party claims and fraud. Record the assumptions and run a range. Insurance may address some categories and exclude or sublimit others.

    The Australian Government’s business insurance overview says cyber cover can include costs associated with extortion, interruption, network or data breaches, recovery and accidental loss or release of personal information. “Can include” is the important phrase; the actual contract controls.

    Read the complete contract stack

    Do not assess a product from the quote summary alone. Obtain and read the Product Disclosure Statement or policy wording, quotation, schedule, endorsements and any proposal or application incorporated into the contract. Confirm which document prevails if terms conflict.

    The schedule normally personalises items such as the insured entity, period, limits, sublimits and excess. Endorsements can add, remove or rewrite cover. Definitions can change the ordinary meaning of terms such as computer system, insured data, security failure, dependent business, claim or loss.

    Business.gov.au’s insurance-management guidance recommends understanding covered events, exclusions, definitions, settlement, excess, cancellation, disclosure duties and the complaints process. Ask a licensed broker or authorised insurer to explain anything unclear and retain the answer in writing.

    Turn coverage headings into questions

    For each relevant loss scenario, ask where and how it is addressed:

    Incident response and recovery

    • Are forensic investigation, legal triage, data restoration, crisis communications and customer support covered?
    • Must the insured use a panel provider or obtain consent before spending?
    • Are emergency costs before consent treated differently?
    • Does restoration include only data, or also software, configuration and improved replacement?

    Business interruption

    • What event triggers cover, when does the waiting period start, and how is loss calculated?
    • Are outages at named cloud, software or managed-service providers included?
    • Is there a maximum indemnity period or sublimit for dependent business interruption?

    Privacy, network and media liability

    • Which third-party allegations and defence costs are included?
    • Are defence costs inside or outside the limit?
    • How are investigations, notification expenses, contractual liability and payment-card assessments treated?
    • Are fines or penalties covered only where legally insurable, or excluded?

    Extortion, fraud and funds transfer

    • Does the policy cover response advice and negotiation, and what legal, sanctions and consent conditions apply?
    • Is fraudulent transfer or social-engineering loss included, separately sublimited or excluded?
    • Does a loss caused by impersonation without a network intrusion meet the definition of a cyber event?

    Never assume that ransomware payment is lawful, advisable or recoverable. Escalate to the insurer’s response service, legal adviser and relevant authorities rather than improvising.

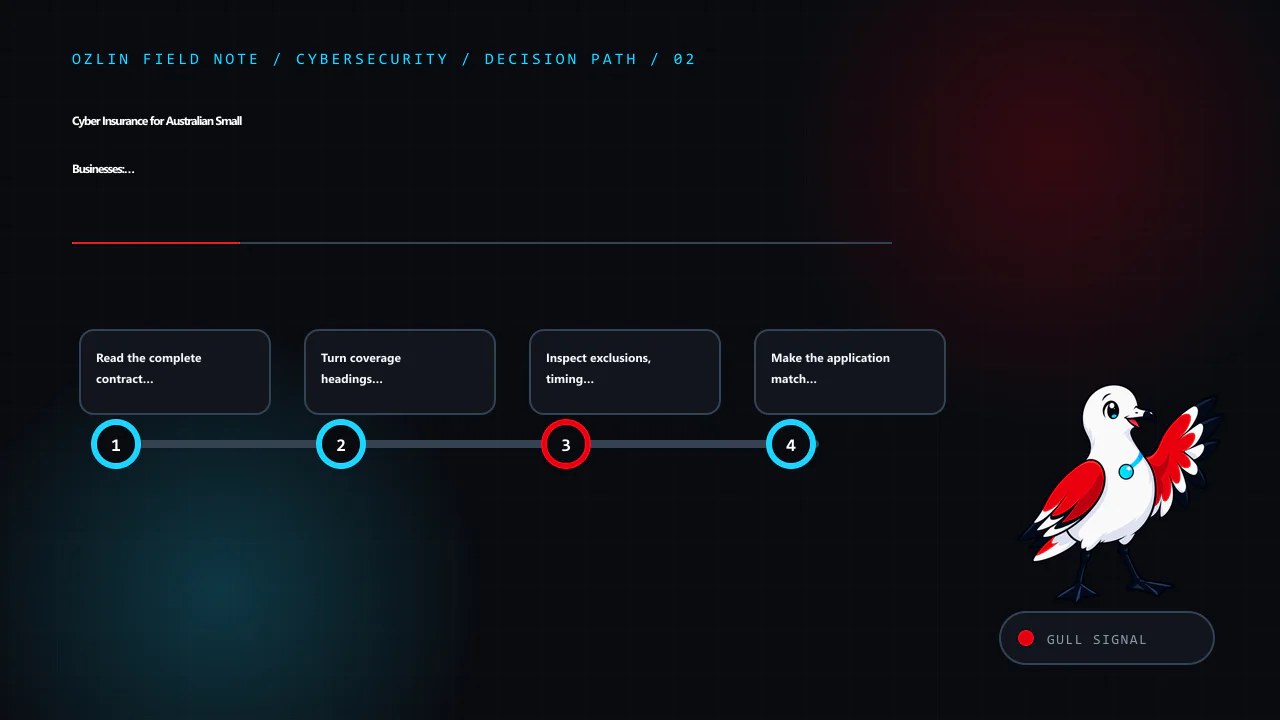
    Decision path for Cyber Insurance for Australian Small Businesses: A Reading Checklist, covering Read the complete contract stack, Turn coverage headings into questions, Inspect exclusions, timing and aggregation and re…
    Decision path: Read the complete contract stack; Turn coverage headings into questions; Inspect exclusions, timing and aggregation; Make the application match reality.

    Inspect exclusions, timing and aggregation

    Compare exclusions against the risk map. Common areas requiring close reading include prior known circumstances, unsupported software, failure to maintain declared controls, infrastructure or utility failure, war or cyber-operation wording, bodily injury or property damage, professional services, intellectual property, contractually assumed liability and conduct exclusions. Their scope varies; the label alone is not enough.

    Ask which sections are claims-made and notified, what counts as a claim or circumstance, whether a retroactive date applies and how soon notice must be given. Check territorial and jurisdiction limits. Understand whether multiple events are aggregated into one claim, one excess or one limit.

    Compare the main aggregate limit with every sublimit. A policy advertised with a large headline limit may apply much smaller amounts to social engineering, dependent providers, restoration, notification, reputational harm or voluntary shutdown. Record waiting periods, excesses and coinsurance as well as dollars.

    Make the application match reality

    Insurance applications may ask about multi-factor authentication, backups, endpoint protection, patching, privileged access, remote access, email controls, training and incident history. Answer accurately, identify uncertainty and keep evidence. Do not check “yes” because a control exists somewhere; confirm its scope, enforcement and exceptions.

    Maintain those controls after inception and notify the broker or insurer of material changes when the contract requires it. Keep versioned network diagrams, asset records, backup and restore tests, security policies, training records and remediation tickets. These artefacts support operations first and may also help explain a claim.

    ASD’s Australian Cyber Security Centre recommends small businesses start with multi-factor authentication, updates and backups, then build further resilience through its Small Business Cyber Security Guide. Insurance is one treatment alongside those controls, not an alternative to them.

    Rehearse notification before an incident

    Store the policy number, broker, insurer hotline, panel contacts and notification method somewhere available when normal systems are down. Define who can call, who preserves evidence and who approves emergency work. The first technical instinct—rebuilding or deleting—can destroy evidence or conflict with response instructions.

    Privacy obligations depend on the organisation and activity. Most Australian small businesses with annual turnover of $3 million or less are not covered by the Privacy Act, but important exceptions apply. Use the OAIC’s small-business guidance and obtain advice rather than assuming an exemption.

    For entities covered by the Notifiable Data Breaches scheme, notification is required for eligible breaches likely to cause serious harm when remedial action has not removed that likely risk. The OAIC’s NDB guidance explains the threshold and assessment process. Contractual, sector and insurer notice requirements can be different and earlier.

    At renewal, compare changed systems, revenue, data, providers, incidents and contract obligations against the wording. Verify the insurer on APRA’s general-insurer register and a broker or other financial-services provider through ASIC’s professional registers where applicable.

    For help improving the technical controls and incident evidence behind an application, see Ozlin Info’s cybersecurity services or contact Ozlin Info.

    Related reading: cybersecurity priorities for Australian SMEs and a phishing response playbook.


    Control and evidence map for Cyber Insurance for Australian Small Businesses: A Reading Checklist, covering Inspect exclusions, timing and aggregation, Make the application match reality, Rehearse notification before an…
    Control and evidence map: Inspect exclusions, timing and aggregation; Make the application match reality; Rehearse notification before an incident; General-information disclaimer.

    General-information disclaimer

    This article provides general information only and is not financial product advice, legal advice, insurance advice or a statement about any Ozlin Info policy. Cover depends on the complete wording, schedule, endorsements, facts and applicable law. Consult a licensed broker, authorised insurer and qualified legal or privacy adviser for your circumstances.

    AI-assistance disclosure

    AI tools assisted with source discovery, outlining and copyediting. A human reviewer must verify every policy, legal, privacy and incident-response statement against current official guidance and the complete proposed contract before publication or use.

    Practical checklist for Cyber Insurance for Australian Small Businesses: A Reading Checklist, covering Rehearse notification before an incident, General-information disclaimer, AI-assistance disclosure and related revie…
    Practical checklist: Rehearse notification before an incident; General-information disclaimer; AI-assistance disclosure; Primary sources checked.

    Primary sources checked

    Source access date: 29 August 2026.
  • Phishing Response Playbook for Australian Small Businesses

    Phishing Response Playbook for Australian Small Businesses

    Reviewed: 13 September 2026 · Next review: 13 December 2026
    Author: Ozlin Info Editorial Team · Human review: Lin (accountable human); Codex assisted

    The most valuable phishing response is not a perfect employee who never makes a mistake. It is a business process that makes suspicious activity easy to report, limits what one mistake can expose and helps the response team act quickly without blame.

    Phishing is broader than a poorly written email. Socially engineered messages can arrive by email, SMS, chat, QR code or phone and may ask a person to open a file, visit a website, share credentials or verification codes, install software, approve an MFA prompt, transfer money or change bank details. ASD's Australian Cyber Security Centre (ASD's ACSC) updated its guidance in April 2026 to include unsolicited “support”, device-linking requests, QR codes and registration or verification codes (ASD's ACSC detecting socially engineered messages).

    Good spelling is not evidence that a message is legitimate. Treat context and requested action as more important than appearance.

    Before an incident: make the safe action the easy action

    Give every worker one obvious reporting route—a mail-client report button, a dedicated address or a help-desk option—and tell them what happens next. A report should be welcomed even when the message proves harmless. If people fear embarrassment or punishment, they may hide the event until damage becomes harder to contain.

    Put independent verification into business processes, especially payments, payroll, credential resets, customer-data exports and changes to supplier details. A callback must use a number obtained from an existing trusted record or official website, not the number in the suspicious message. ASD's business email compromise guidance recommends a clear and consistent process to verify payment and sensitive-information requests (ASD's ACSC BEC guidance).

    Technical layers still matter: MFA, unique credentials in a password manager, restricted administrator access, supported updates, endpoint protection, email filtering and domain authentication. None proves that every delivered message is safe. Pair controls with logging and an escalation path so the business can investigate account changes, new sessions and unusual mailbox rules.

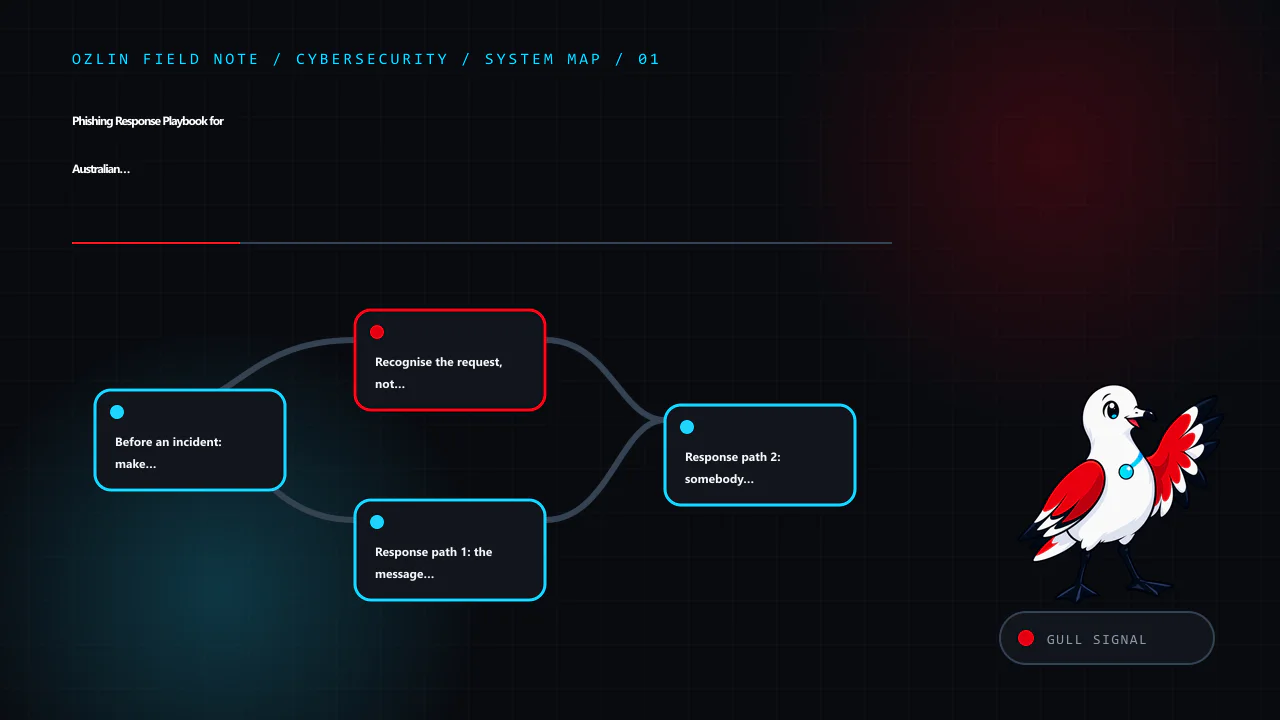
    Article map for Phishing Response Playbook for Australian Small Businesses, covering Before an incident: make the safe action the easy action, Recognise the request, not just the design, Response path 1: the message arr…
    Article map: Before an incident: make the safe action the easy action; Recognise the request, not just the design; Response path 1: the message arrived, but nobody interacted; Response path 2: somebody clicked a link, but entered nothi….

    Recognise the request, not just the design

    Pause when a message introduces one or more of these conditions:

    • an unexpected change to bank or supplier details;
    • urgency, secrecy, authority or pressure to bypass a normal approval;
    • an unexpected attachment, shared document, QR code or login link;
    • a request for a password, recovery code, MFA approval or remote access;
    • “support” that contacts you first and asks you to install software or link a device;
    • a sender name that looks familiar but a domain, reply address or conversation context that does not; or
    • a request that is plausible but unusual for that person, customer or supplier.

    When uncertain, go independently to the organisation's official website or app, or call a known number. ASD advises users not to enter credentials into a website reached through a message link and to use an out-of-band contact method to confirm unexpected attachments or requests (ASD's ACSC detection guidance).

    Response path 1: the message arrived, but nobody interacted

    Do not reply, click, scan the QR code, call a supplied number or forward the message casually. Use the organisation's reporting method. Where an IT or security team may need headers or the original item, follow its preservation instructions rather than deleting the evidence immediately; ASD's guidance tells workers who suspect a socially engineered message not to delete or forward it, but to contact their IT help desk or security team.

    The person handling the report should check whether other staff received the same campaign, block known malicious indicators where appropriate and warn the specific people who may be targeted. Avoid sending a clickable malicious link in the warning.

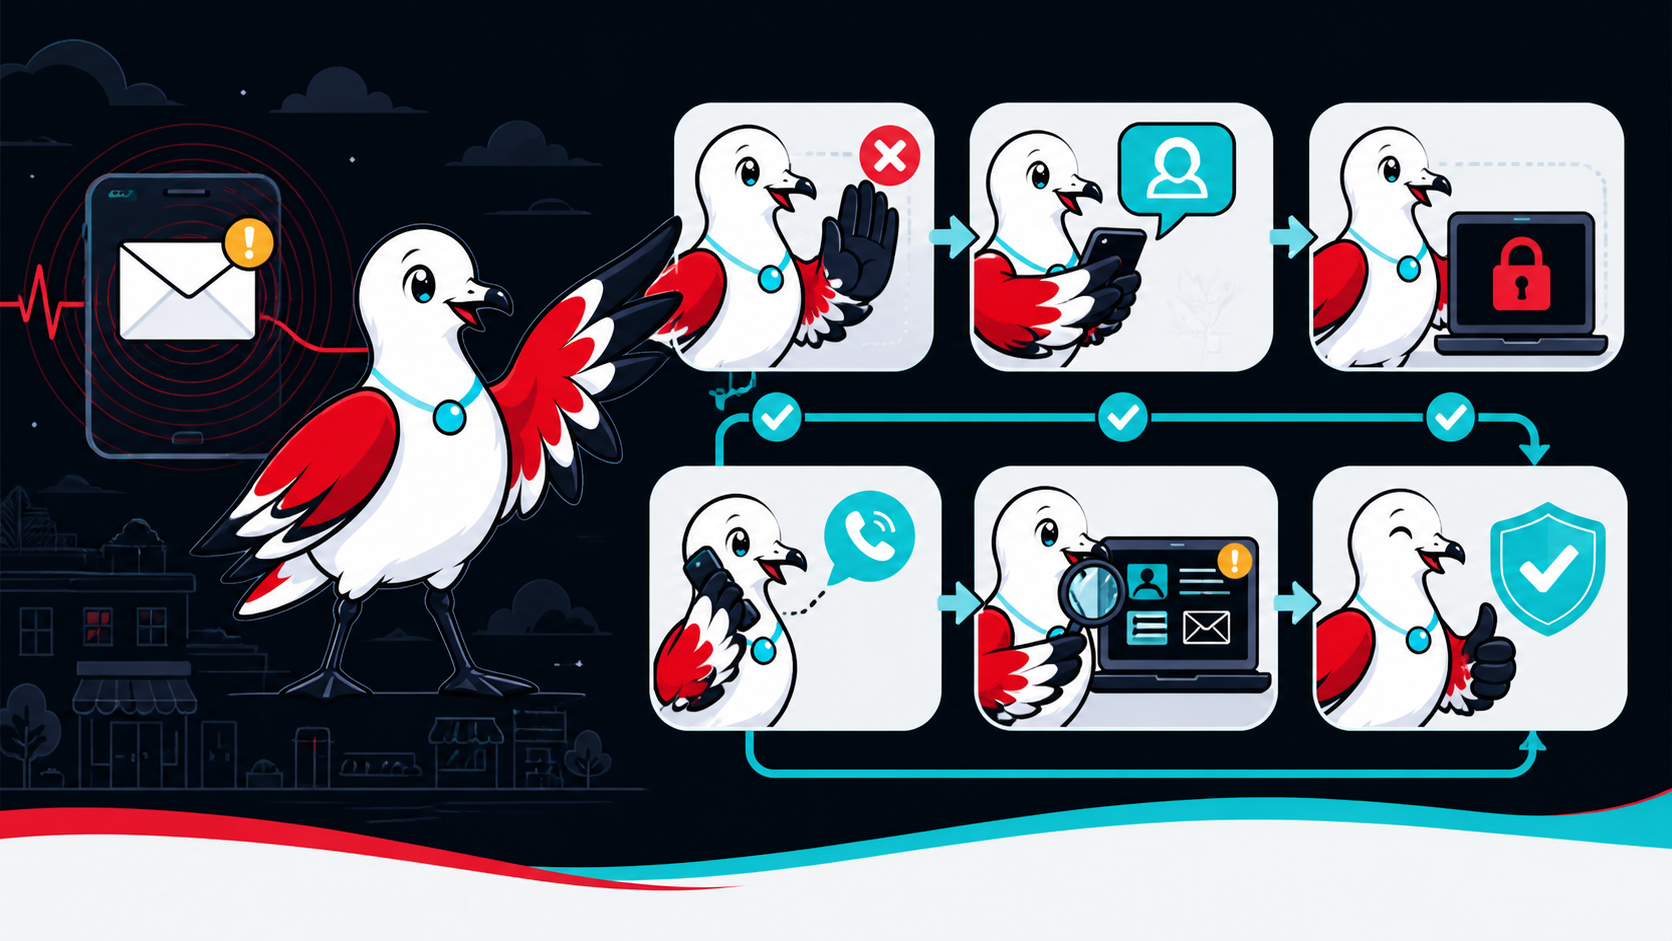
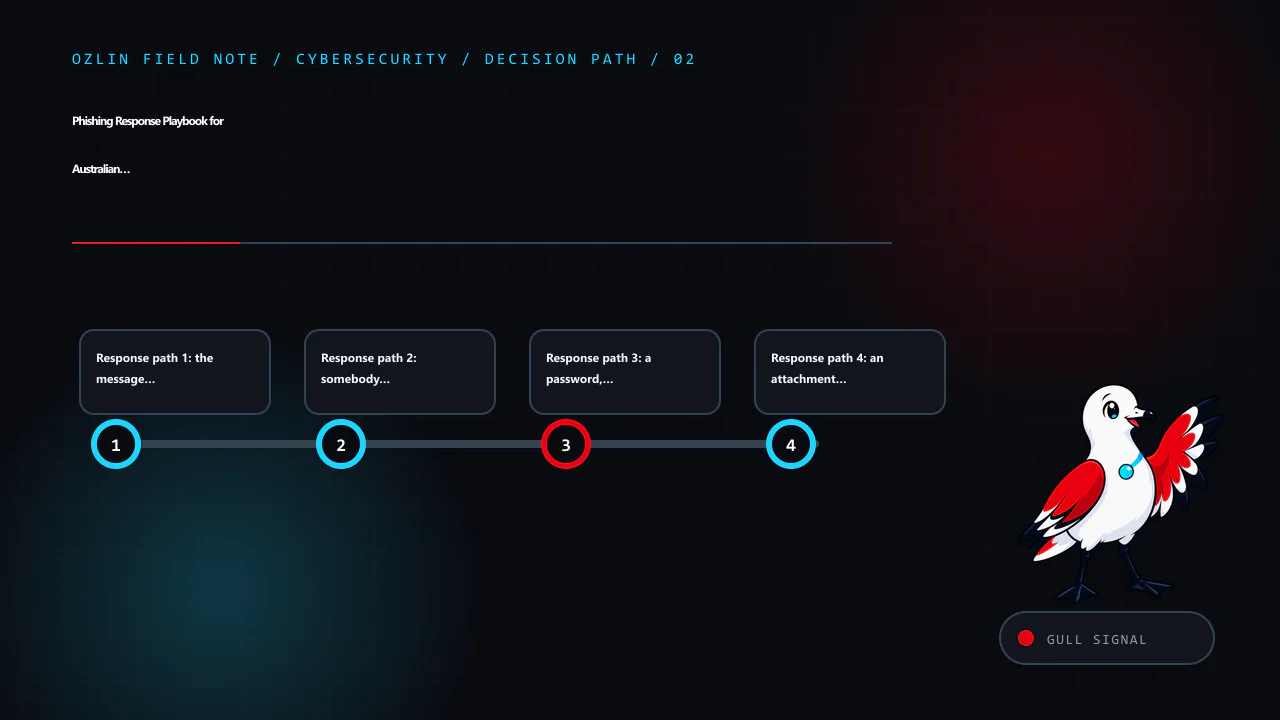
    Decision path for Phishing Response Playbook for Australian Small Businesses, covering Response path 1: the message arrived, but nobody interacted, Response path 2: somebody clicked a link, but entered nothi…, Response…
    Decision path: Response path 1: the message arrived, but nobody interacted; Response path 2: somebody clicked a link, but entered nothi…; Response path 3: a password, code or MFA approval was provi…; Response path 4: an attachment or remote-support tool may h….

    Response path 2: somebody clicked a link, but entered nothing

    Report the event immediately and record the time, device, account, message and observed page. A click does not by itself establish that the device or account is compromised, but it warrants triage. Do not keep browsing the page to “test” it.

    If a download ran, an attachment opened, software was installed, a browser extension appeared or the device behaves unexpectedly, stop using the device and contact the response owner. Isolate it from normal business connectivity if the response procedure calls for that. Do not use a potentially compromised device to reset important credentials.

    Response path 3: a password, code or MFA approval was provided

    Treat the account as potentially compromised. From a known-clean device and trusted route to the service:

    1. contact the internal response owner or provider;
    2. change the affected credential and any reused credential;
    3. sign out or revoke other sessions and tokens where the service supports it;
    4. verify recovery email addresses, phone numbers, MFA methods and delegated access;
    5. check for new mailbox forwarding rules, filters, application permissions and administrators;
    6. review available sign-in and audit logs; and
    7. preserve a timeline of what was observed and changed.

    ASD's recovery guidance for business email compromise specifically includes changing the passphrase, checking recovery details, signing out other sessions and enabling MFA (ASD's ACSC BEC recovery guidance). If the account can reset other services, assess those services too.

    Response path 4: an attachment or remote-support tool may have executed

    Separate the affected device from business networks without wiping or “cleaning” it first, unless qualified responders direct otherwise. Record what ran and when. Preservation matters because logs and files may be needed to establish scope. The response team can then decide whether to collect evidence, scan, rebuild or restore the device.

    Change exposed credentials from a clean device, not from the suspected endpoint. Review access from the device to file shares, cloud storage, password stores and administrative systems. A factory reset or antivirus scan alone does not establish what data or credentials were accessed.

    Control and evidence map for Phishing Response Playbook for Australian Small Businesses, covering Response path 4: an attachment or remote-support tool may h…, Response path 5: money, bank details or identity informatio…
    Control and evidence map: Response path 4: an attachment or remote-support tool may h…; Response path 5: money, bank details or identity informatio…; Assess privacy and notification obligations—do not guess; Run a 20-minute rehearsal.

    Response path 5: money, bank details or identity information may be at risk

    Contact the financial institution immediately using an independently verified number. Ask about recalling or stopping the transaction and securing affected accounts. Notify the legitimate supplier or customer through a trusted channel. Preserve invoices, account details, message headers and the sequence of approvals; do not continue negotiating with the suspected sender.

    Report cybercrime through ReportCyber or seek help from the 24/7 Australian Cyber Security Hotline on 1300 CYBER1 (1300 292 371). ASD also directs people whose identity information is at risk towards relevant support services, including IDCARE (ASD's ACSC hacking recovery guidance). Call 000 if there is an immediate threat to life or safety.

    Assess privacy and notification obligations—do not guess

    Determine what information and people may be affected, who may have accessed it, whether access was prevented or remediated and what harm could result. Preserve the basis for the decision.

    Not every phishing event is an eligible data breach. For entities covered by the Notifiable Data Breaches scheme, however, reasonable grounds to suspect a serious breach trigger an assessment obligation. The OAIC says the entity must take all reasonable steps to complete that assessment within 30 calendar days and should treat that period as a maximum, not a waiting period (OAIC data-breach preparation and response guide). Obtain appropriate legal or privacy advice when the facts or obligations are unclear.

    Run a 20-minute rehearsal

    Use a fictional supplier email requesting an urgent bank-detail change. Ask the team:

    • How does the recipient report it?
    • Who independently verifies the request?
    • Who checks accounts, sessions and mail rules?
    • Who calls the bank and supplier if payment was made?
    • Where is evidence recorded?
    • Who assesses customers, contracts and privacy obligations?
    • What continues if email is temporarily unavailable?

    Record owners and gaps, then repeat the exercise after changes. This article supports the broader Australian SME cybersecurity baseline. For a scoped review of account, email and incident-response controls, see Ozlin Info's cybersecurity uplift service or contact Ozlin Info.


    Practical checklist for Phishing Response Playbook for Australian Small Businesses, covering Run a 20-minute rehearsal, General-information disclaimer, AI-assistance disclosure and related review points.
    Practical checklist: Run a 20-minute rehearsal; General-information disclaimer; AI-assistance disclosure; Primary sources checked.

    General-information disclaimer

    This article provides general information only. It is not legal, privacy, insurance, financial, forensic or incident-response advice. Do not delay urgent assistance to follow a generic checklist. The appropriate actions depend on the message, device, accounts, data, contracts and active threat.

    Limitations: This checklist cannot determine whether a message or device is safe and is not forensic or legal advice. Active incidents require qualified responders; steps and notification duties depend on the facts, accounts, data and jurisdiction.

    AI-assistance disclosure

    AI tools assisted with outlining and copyediting this article. The recorded editorial review and review schedule appear at the start of this article. Verify current sources and project-specific assumptions before relying on this guidance. No claim is made that following this playbook will prevent or fully contain an incident.

    Primary sources checked

    Source access date: 28 August 2026.

  • Cybersecurity for Australian SMEs: 8 Practical Priorities for 2026

    Cybersecurity for Australian SMEs: 8 Practical Priorities for 2026

    Reviewed: 13 September 2026 · Next review: 13 December 2026
    Author: Ozlin Info Editorial Team · Human review: Lin (accountable human); Codex assisted

    Cybersecurity for a small business is not a shopping list of products. It is the ongoing work of deciding what matters, reducing likely paths to harm, noticing trouble and recovering without losing control of the business.

    That distinction matters. No product, consultant or checklist can make an organisation immune to cyber incidents. A useful baseline should instead lower risk, produce evidence that important safeguards work and give people a rehearsed way to respond.

    For Australian small businesses beginning this work, the Australian Signals Directorate's Australian Cyber Security Centre (ASD's ACSC) recommends three immediate measures: turn on multi-factor authentication, update software and back up information. Its small-business guide then points organisations towards Maturity Level One of the Essential Eight after they have covered the basics (ASD's ACSC small-business guide). The eight priorities below turn that advice into a manageable business baseline.

    1. Identify the services and information that cannot be casually lost

    Start with business impact, not tools. List the systems that support quoting, invoicing, customer communication, delivery, payroll, your website and access to money. Record who owns each system, where its data is held, which supplier operates it and what the business would do if it were unavailable for a day or a week.

    Also identify sensitive information: customer records, identity documents, credentials, payment-related records, source code and confidential client material. This does not need to begin as a complex asset-management platform; a maintained register is more useful than an expensive dashboard nobody trusts.

    NIST's Cybersecurity Framework 2.0 is designed for organisations of any size and treats cybersecurity as a business-risk discipline. Its six concurrent functions are Govern, Identify, Protect, Detect, Respond and Recover (NIST CSF 2.0). That sequence is a useful test: if a proposal only talks about prevention, it is incomplete.

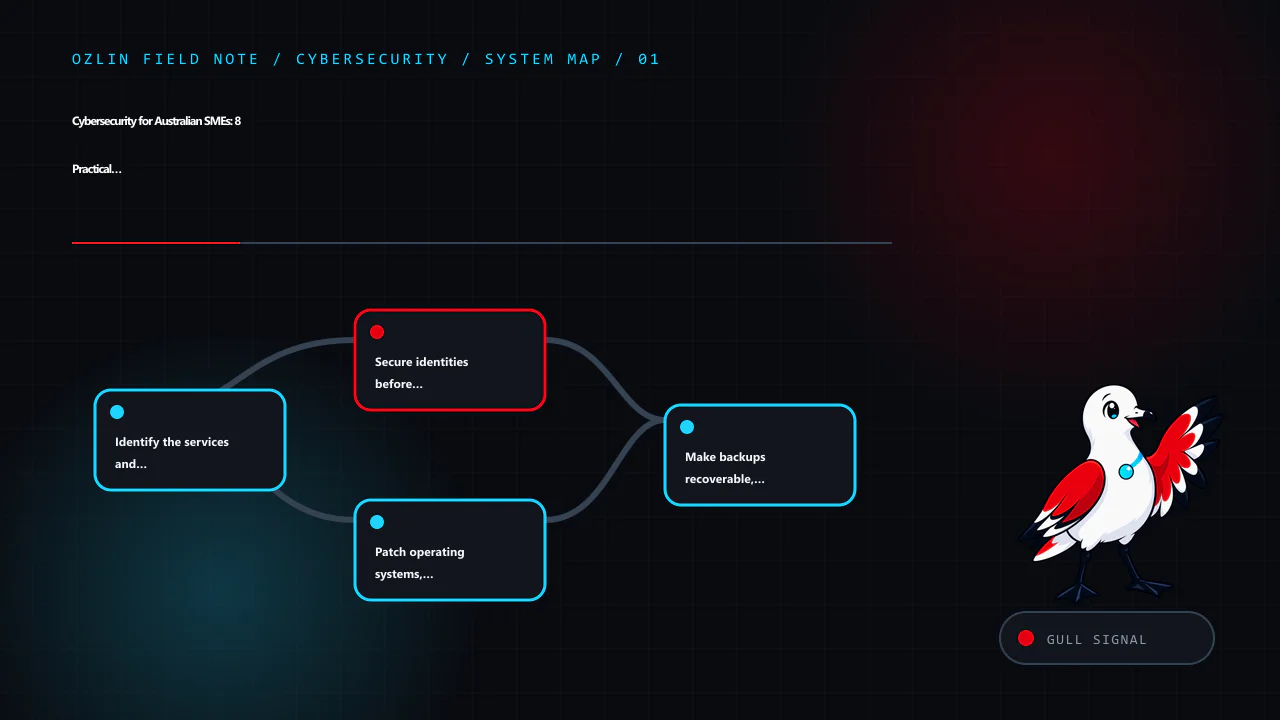
    Article map for Cybersecurity for Australian SMEs: 8 Practical Priorities for 2026, covering Identify the services and information that cannot be casual…, Secure identities before adding more software, Patch operating s…
    Article map: Identify the services and information that cannot be casual…; Secure identities before adding more software; Patch operating systems, applications and internet-facing s…; Make backups recoverable, not merely present.

    2. Secure identities before adding more software

    Email, cloud administration, banking, accounting, domain registration, website administration and password-manager accounts deserve priority. Use a unique account for each person, remove access promptly when it is no longer required and keep routine work separate from privileged administration where practical.

    Enable MFA, beginning with accounts that can expose sensitive information or reset other accounts. A business password manager can help create and store unique credentials without relying on memory. ASD's 2025 small-business device and account guidance specifically includes MFA, password managers, backups and updates as practical steps (ASD's ACSC device and account guidance).

    MFA reduces risk; it does not make every sign-in safe. Staff should still reject unexpected approval prompts, never disclose one-time codes, and report a suspicious prompt quickly.

    3. Patch operating systems, applications and internet-facing services

    Turn on supported automatic updates where this fits the system, and maintain a process for software that requires testing or manual deployment. Include browsers, plugins, mobile devices, network equipment, website components and cloud integrations—not only desktop operating systems.

    For a more formal target, use the current Essential Eight maturity model and assess against its evidence requirements rather than copying an old patch timetable from a blog post. ASD notes that the model changes as malicious techniques change and encourages use of the latest version (Essential Eight maturity model FAQ). Unsupported systems should have an upgrade or retirement plan, with compensating controls assessed in the meantime.

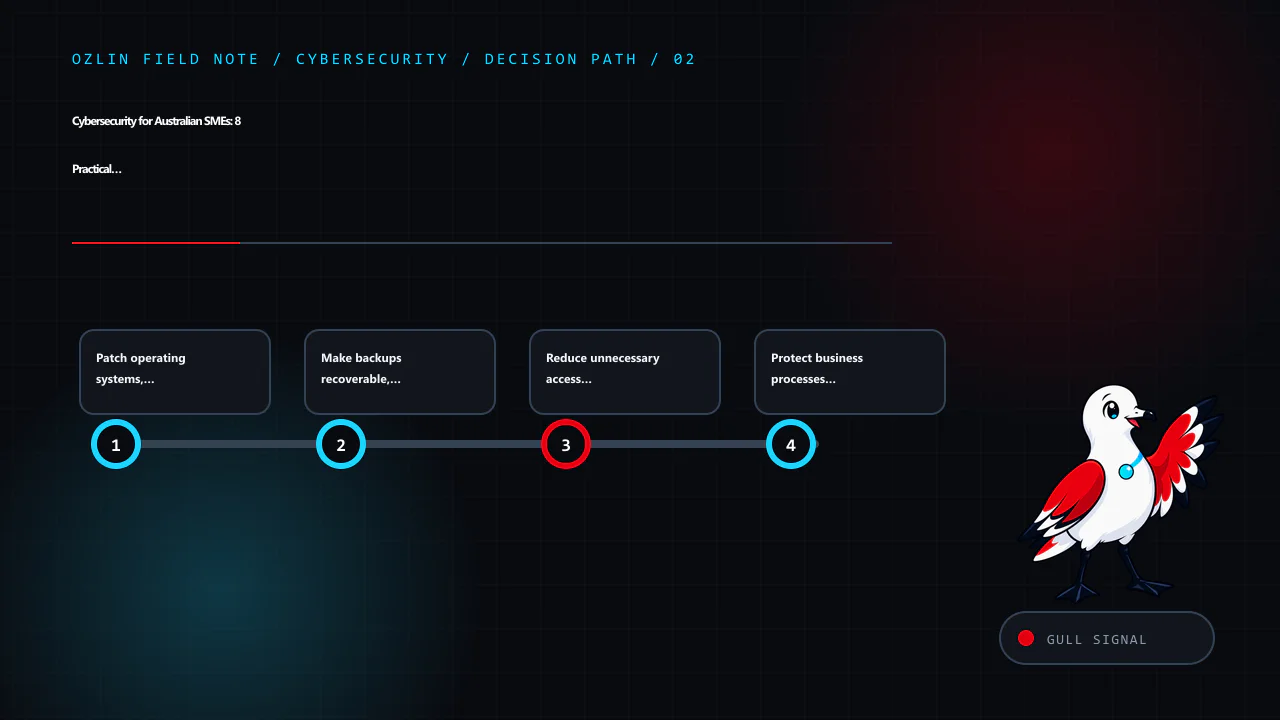
    Decision path for Cybersecurity for Australian SMEs: 8 Practical Priorities for 2026, covering Patch operating systems, applications and internet-facing s…, Make backups recoverable, not merely present, Reduce unnecessa…
    Decision path: Patch operating systems, applications and internet-facing s…; Make backups recoverable, not merely present; Reduce unnecessary access and data exposure; Protect business processes from phishing and payment fraud.

    4. Make backups recoverable, not merely present

    Decide what must be backed up, how often, how long it must be retained and how quickly it must be restored. Protect backup administration separately from ordinary user accounts and design the backup location so a compromised user or device cannot silently alter every recovery copy.

    Most importantly, test restoration. ASD's technical example says restoration of systems, software and important data should be tested as part of recovery exercises, and unprivileged accounts should be prevented from modifying or deleting backups (ASD's ACSC regular-backup example). Record the result, the time taken and anything that was missing.

    5. Reduce unnecessary access and data exposure

    Give people and integrations only the access required for their role. Review shared accounts, former-worker access, public links, API keys, administrator memberships and third-party app permissions. Separate guest Wi-Fi and untrusted devices from business systems where the environment warrants it.

    Collect and retain only information the business can justify. Data minimisation is not a substitute for security, but less unnecessary data means less information available to expose. Map important data flows, including transfers to SaaS suppliers and contractors, and record contractual, regulatory and privacy obligations that affect them.

    6. Protect business processes from phishing and payment fraud

    Awareness training works best when paired with a process. Give workers a simple way to report suspicious messages and require independent verification for new bank details, unusual payments or requests to bypass approval. Use a known phone number or another separately verified channel—not contact details supplied in the message.

    ASD's business email compromise guidance recommends consistent verification for payment and sensitive-information requests and highlights unexpected bank-detail changes, urgency and requests to circumvent normal processes as warning signs (ASD's ACSC BEC guidance). See the related phishing response playbook for the immediate response steps.

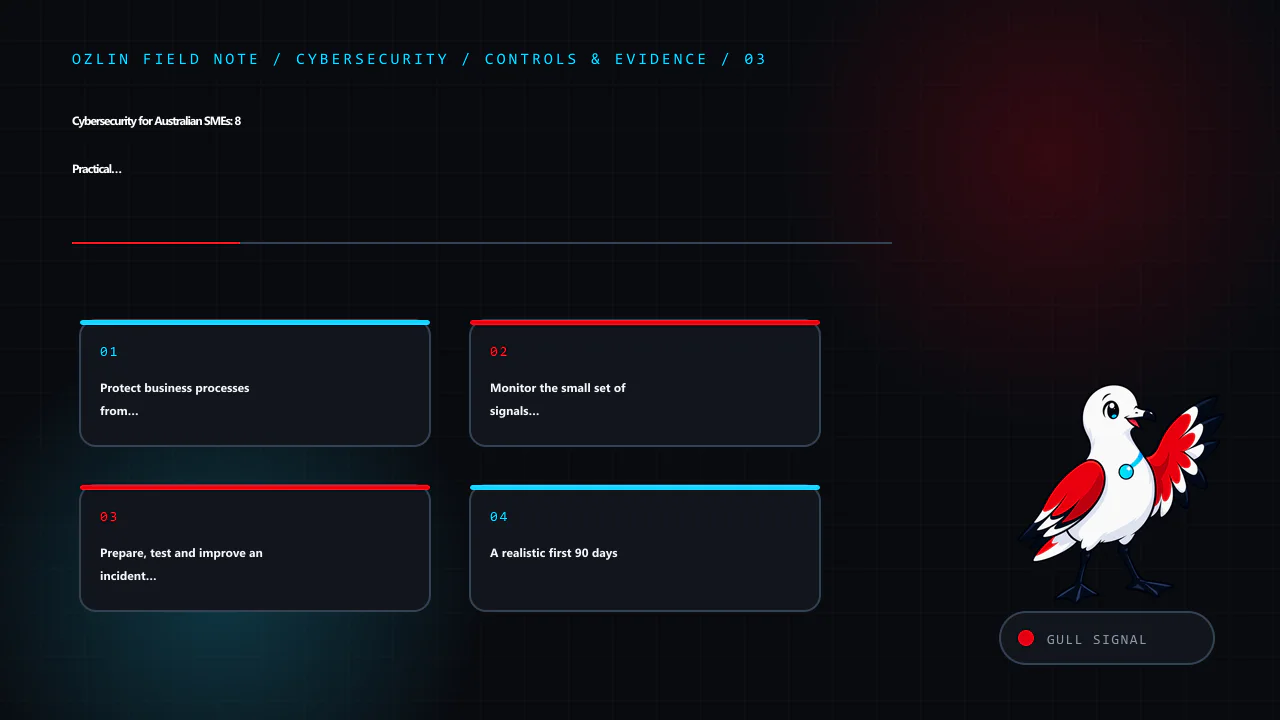
    Control and evidence map for Cybersecurity for Australian SMEs: 8 Practical Priorities for 2026, covering Protect business processes from phishing and payment fraud, Monitor the small set of signals that matter, Prepare…
    Control and evidence map: Protect business processes from phishing and payment fraud; Monitor the small set of signals that matter; Prepare, test and improve an incident plan; A realistic first 90 days.

    7. Monitor the small set of signals that matter

    Detection should match the systems identified as critical. Useful starting signals can include privileged sign-ins, new MFA methods, mailbox forwarding-rule changes, new administrators, unexpected exports, backup failures, website changes and security alerts from managed services.

    Someone must own the alerts, know the expected response time and be able to reach the relevant supplier. Retain logs for a period that supports investigation and contractual needs, while avoiding indefinite retention without a purpose. Test whether alerts are delivered and acted upon; a configured alert that nobody reads is not an operating control.

    8. Prepare, test and improve an incident plan

    A concise plan should name the incident lead, decision-makers, technical contacts, insurer or broker contact, legal/privacy support, bank contact and key suppliers. Include an offline copy. Define how staff will report concerns, how affected access may be contained, who preserves evidence, how essential work continues and who approves external communication.

    ASD says organisations should tailor, regularly test and review their cyber incident response plans (ASD's ACSC incident-response planning guidance). Notification duties depend on the organisation and the facts. For entities covered by the Notifiable Data Breaches scheme, the OAIC's current quick reference separates response into contain, assess, notify if required, and review (OAIC data-breach quick reference). Do not assume every security event is notifiable—or that no notification is required—without an appropriate assessment.

    A realistic first 90 days

    Days 1–30: name an owner; inventory critical services, data and suppliers; enable MFA on high-impact accounts; remove stale access; turn on supported updates; verify that backups are completing.

    Days 31–60: perform a restore test; review administrator access and email rules; establish payment-change verification; define the alert and escalation path; document important supplier contacts.

    Days 61–90: run a short incident exercise; record gaps and owners; compare current practices with the latest Essential Eight Maturity Level One requirements; set a funded improvement backlog based on risk.

    Progress should be evidenced by results: a successful restore, an access review, a resolved alert test and a timed incident exercise. A completed questionnaire alone does not prove that controls operate effectively.

    Practical checklist for Cybersecurity for Australian SMEs: 8 Practical Priorities for 2026, covering A realistic first 90 days, General-information disclaimer, AI-assistance disclosure and related review points.
    Practical checklist: A realistic first 90 days; General-information disclaimer; AI-assistance disclosure; Primary sources checked.

    Turn the priorities into an evidence register

    Copy this worksheet into your own working document. Use one row per critical service where responsibilities differ. Enter the responsible person, the latest evidence date, the remaining gap and the next action date. Leave untested items marked Not verified; a planned control is not a completed test. This worksheet organises the priorities above, not an Essential Eight assessment or a claim of compliance.

    PriorityEvidence to recordYour owner, date and next action
    Critical servicesService and data inventory; supplier and recovery contact; business impact of an outage.Not verified — complete locally.
    Accounts and accessMFA coverage, administrator list and result of the latest stale-access review. Do not record passwords or recovery codes here.Not verified — complete locally.
    UpdatesUpdate status, unsupported components, exceptions and the person responsible for each exception.Not verified — complete locally.
    RecoveryRestore-test date, what was restored, elapsed time, missing data and unresolved failures.Not verified — complete locally.
    Data exposureResult of the shared-link, administrator and third-party permission review; unnecessary access removed or awaiting action.Not verified — complete locally.
    Payment verificationDocumented independent-verification route, its owner and how suspicious requests are reported.Not verified — complete locally.
    AlertsTest alert, recipient, receipt time and recorded response; escalation contact for missed alerts.Not verified — complete locally.
    Incident readinessExercise date, contact-list check, decisions practised, gaps and assigned follow-up actions.Not verified — complete locally.

    At the next review, check whether the evidence still matches the service, its access and its recovery process. Keep sensitive operational records in your controlled workspace, not in public comments or a contact-form submission. Record failures as well as successes so the next action is specific.

    Cyber insurance may transfer some financial risk, subject to policy terms, exclusions and disclosure obligations. It does not replace prevention, detection, response or recovery work. Likewise, a security assessment should describe its scope and limitations; it should not promise that no vulnerability or incident will occur.

    For a scope-first review of accounts, website operations, backups and incident readiness, see Ozlin Info's cybersecurity uplift service or contact Ozlin Info.


    General-information disclaimer

    This article provides general information only. It is not legal, privacy, insurance, financial or incident-response advice, and it is not a complete security standard. Appropriate controls and notification obligations depend on your systems, data, contracts, sector and circumstances. Obtain qualified advice for your organisation and seek urgent assistance when an incident may be active.

    Limitations: This prioritisation is not a full risk assessment, security standard or guarantee. Control effectiveness depends on systems, threat model, people, suppliers, configuration and measured tests.

    AI-assistance disclosure

    AI tools assisted with outlining and copyediting this article. The recorded human review and review schedule appear at the start of the article. No client result or security guarantee is asserted.

    Primary sources checked

    Source access date: 28 August 2026.